

Analysis
Technical cost review
Hosting, tools and ongoing services: we organise up to ten cost items and include the work involved in a possible switch.
Do you really need a rebuild? We review an application's structure and explain what to keep or change.
Your enquiry is non-binding. An order is created only when you accept our quotation .
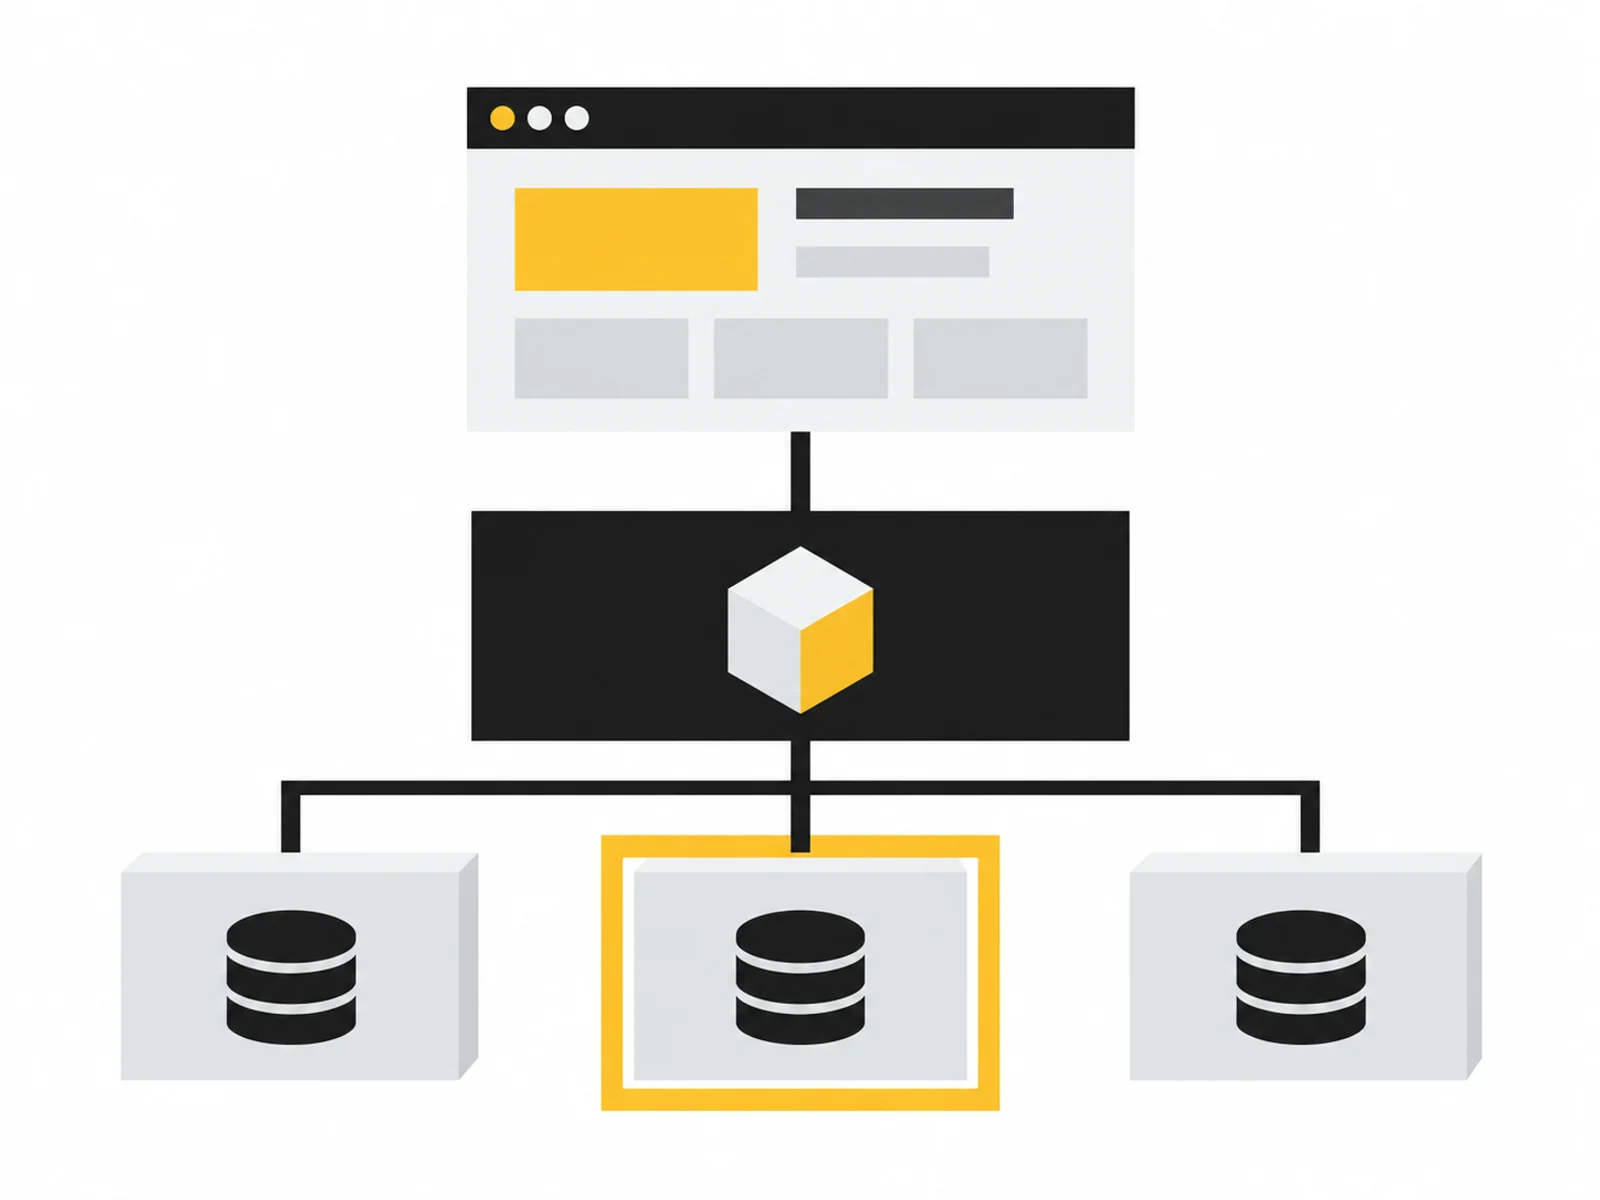
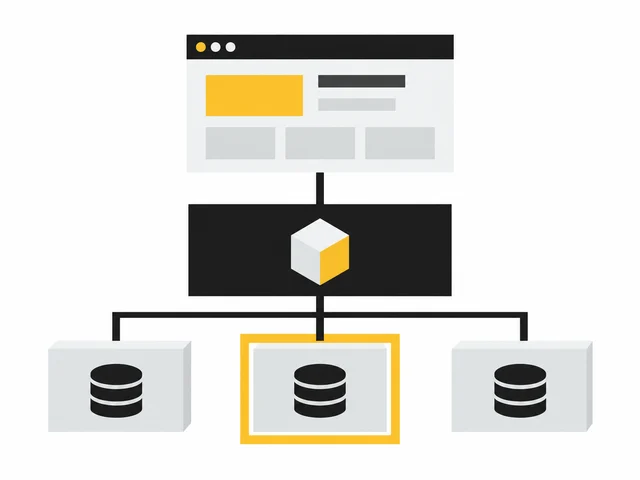
Image 1 of 4
Should your application continue with its existing technology or does it need restructuring? We examine its current structure and compare options against your requirements. The tools used alone do not decide the question.
A technology stack combines the building blocks used for the interface, application logic, data storage and operation. The technology and stack review examines one application and one documented deployment process. You receive a clear overview and reasoned options for your next decision.
Architecture describes how an application's parts work together. Relevant documents and a limited investigation scope are agreed for the review. The focus is maintainability, visible bottlenecks and how changes are deployed. An existing solution may remain the right foundation.
The report distinguishes observations from points needing further investigation. It explains what an option means for your project rather than merely listing current technologies. A complete code review, penetration test or assurance of a particular load is excluded. Required access is agreed only within the defined confidential framework.
Even a small form change touches several services. Your team lacks a connection overview. We trace the relevant structure and examine where dependencies arise.
The prototype runs on its creator's computer. How another person starts, updates and deploys it is barely documented. We examine this foundation for further development.
One developer recommends changing frameworks; another wants to retain the system. We compare suggestions with your requirements, switching effort and existing knowledge.
We define the application, environment and deployment process and gather existing documentation. Missing information is listed as open questions.
We examine the agreed components and their connections for maintainability and visible bottlenecks. Reviewing every line of code and every operating situation is excluded.
We compare what can stay, where a targeted improvement suffices and when replacement would be justified. We also identify unresolved dependencies and required checks. We do not perform a migration.
Discuss options with development and operations. Who can maintain the proposed technology? Which dependency needs resolving first? A component may fit technically yet require extra learning or a new owner.
The results provide neither security approval nor a load guarantee. If recurring expenses are your main problem, the technology cost review offers a different perspective. For a defined first release, the MVP launch check focuses more closely on the existing prototype and its central user journey.
Record a process we can reproduce: which page do you open, what do you click and what happens next? For operational questions, name the tools used and describe how changes reach the server.
Passwords, repository tokens and production data must not be included in the enquiry. We agree required documents and suitable access separately.
What is included, what do you need and what happens after your enquiry?
The process in detail →How it was created is not a blanket reason for exclusion. The application, available documents and technical question matter. We clarify beforehand which parts can be examined within the agreed scope.
The check is not a penetration test and issues no security certificate. Notable technical limitations may be identified, but systematic security investigation requires its own commission and suitable methods.
No. First describe the application and your decision. Passwords and tokens do not belong in the form. Documents or authorised read access needed later are agreed after written commissioning.
No. The investigation scope is limited in advance. An architecture overview and maintainability guidance do not equal reviewing every file in full. Describe particularly critical questions in your enquiry so we can assess suitability.
A tool's name alone does not justify a recommendation. Requirements, existing structure and switching effort must be considered together. The check may therefore conclude that a component should stay, with clearer documentation or targeted improvements to its use.
The check includes analysis and recommendations. Migrations and technical implementation are not automatically included. You can use the results with your team. Any additional implementation scope is separately described and agreed before work starts.
Investigation boundaries and the work window are confirmed in writing before commissioning.
An existing application with a specific technical decision to make Documentation of structure and deployment Read-only documents or authorised repository read access only after commissioning Credentials must not be included in the enquiry. Details are agreed only after written commissioning.
One written follow-up round is included. The service scope lists the analyses, designs or technical changes covered by the package. We agree additional work with you before it begins.
Compare manual data work with integration, maintenance and operation. A clear calculation method for APIs, customer portals and internal applications.
Read the guide ↗Hosting, tools and ongoing services: we organise up to ten cost items and include the work involved in a possible switch.
Your prototype works in the demo. We review one user journey and identify what is missing before your next launch.